Security
The UK Cyber Warning Shows AI Risk Is Moving Into Infrastructure
The UK's National Cyber Security Centre says critical infrastructure faced more than 200 cyber incidents in a year, with state-linked actors behind most of them. Its warning that AI could accelerate the threat by 2028 turns frontier AI into an infrastructure resilience problem.
By Leo W ·
The UK's National Cyber Security Centre says critical national infrastructure and its supporting ecosystem were hit by more than 200 cyber incidents in the year to May, with about three-quarters believed to be linked to state actors. The Guardian reports that NCSC chief Richard Horne warned AI could accelerate the threat, making 2028 a possible crystallization point for more serious AI-enabled attacks.
The warning is important because it grounds AI security in ordinary infrastructure rather than speculative doom. Power plants, hospitals, airports, telecom networks, transport systems, and public services already face state-linked pressure. AI does not have to invent a new threat class to matter. It can make existing reconnaissance, phishing, vulnerability discovery, and operational planning faster.
The Basics Still Matter
Horne's message was not that every attacker now has a superintelligent cyber weapon. It was that organizations tolerate weaknesses during peacetime that could become exploitable during conflict. Weak authentication, poor patching, brittle recovery plans, and slow incident response remain the real terrain on which AI-enhanced attackers will operate.
That distinction matters for boards. AI risk can become paralyzing if it is framed only as a future model capability problem. The practical response is more concrete: know critical systems, harden identity, monitor suppliers, rehearse recovery, remove unsupported assets, and treat resilience as an operating requirement rather than a compliance exercise.
AI Compresses The Attack Cycle
The most likely near-term impact of AI is cycle-time compression. Attackers can generate lure variants, summarize stolen material, triage vulnerability leads, translate technical documentation, and automate parts of reconnaissance. Defenders can use AI too, but the organizations most exposed are often the least able to modernize quickly.
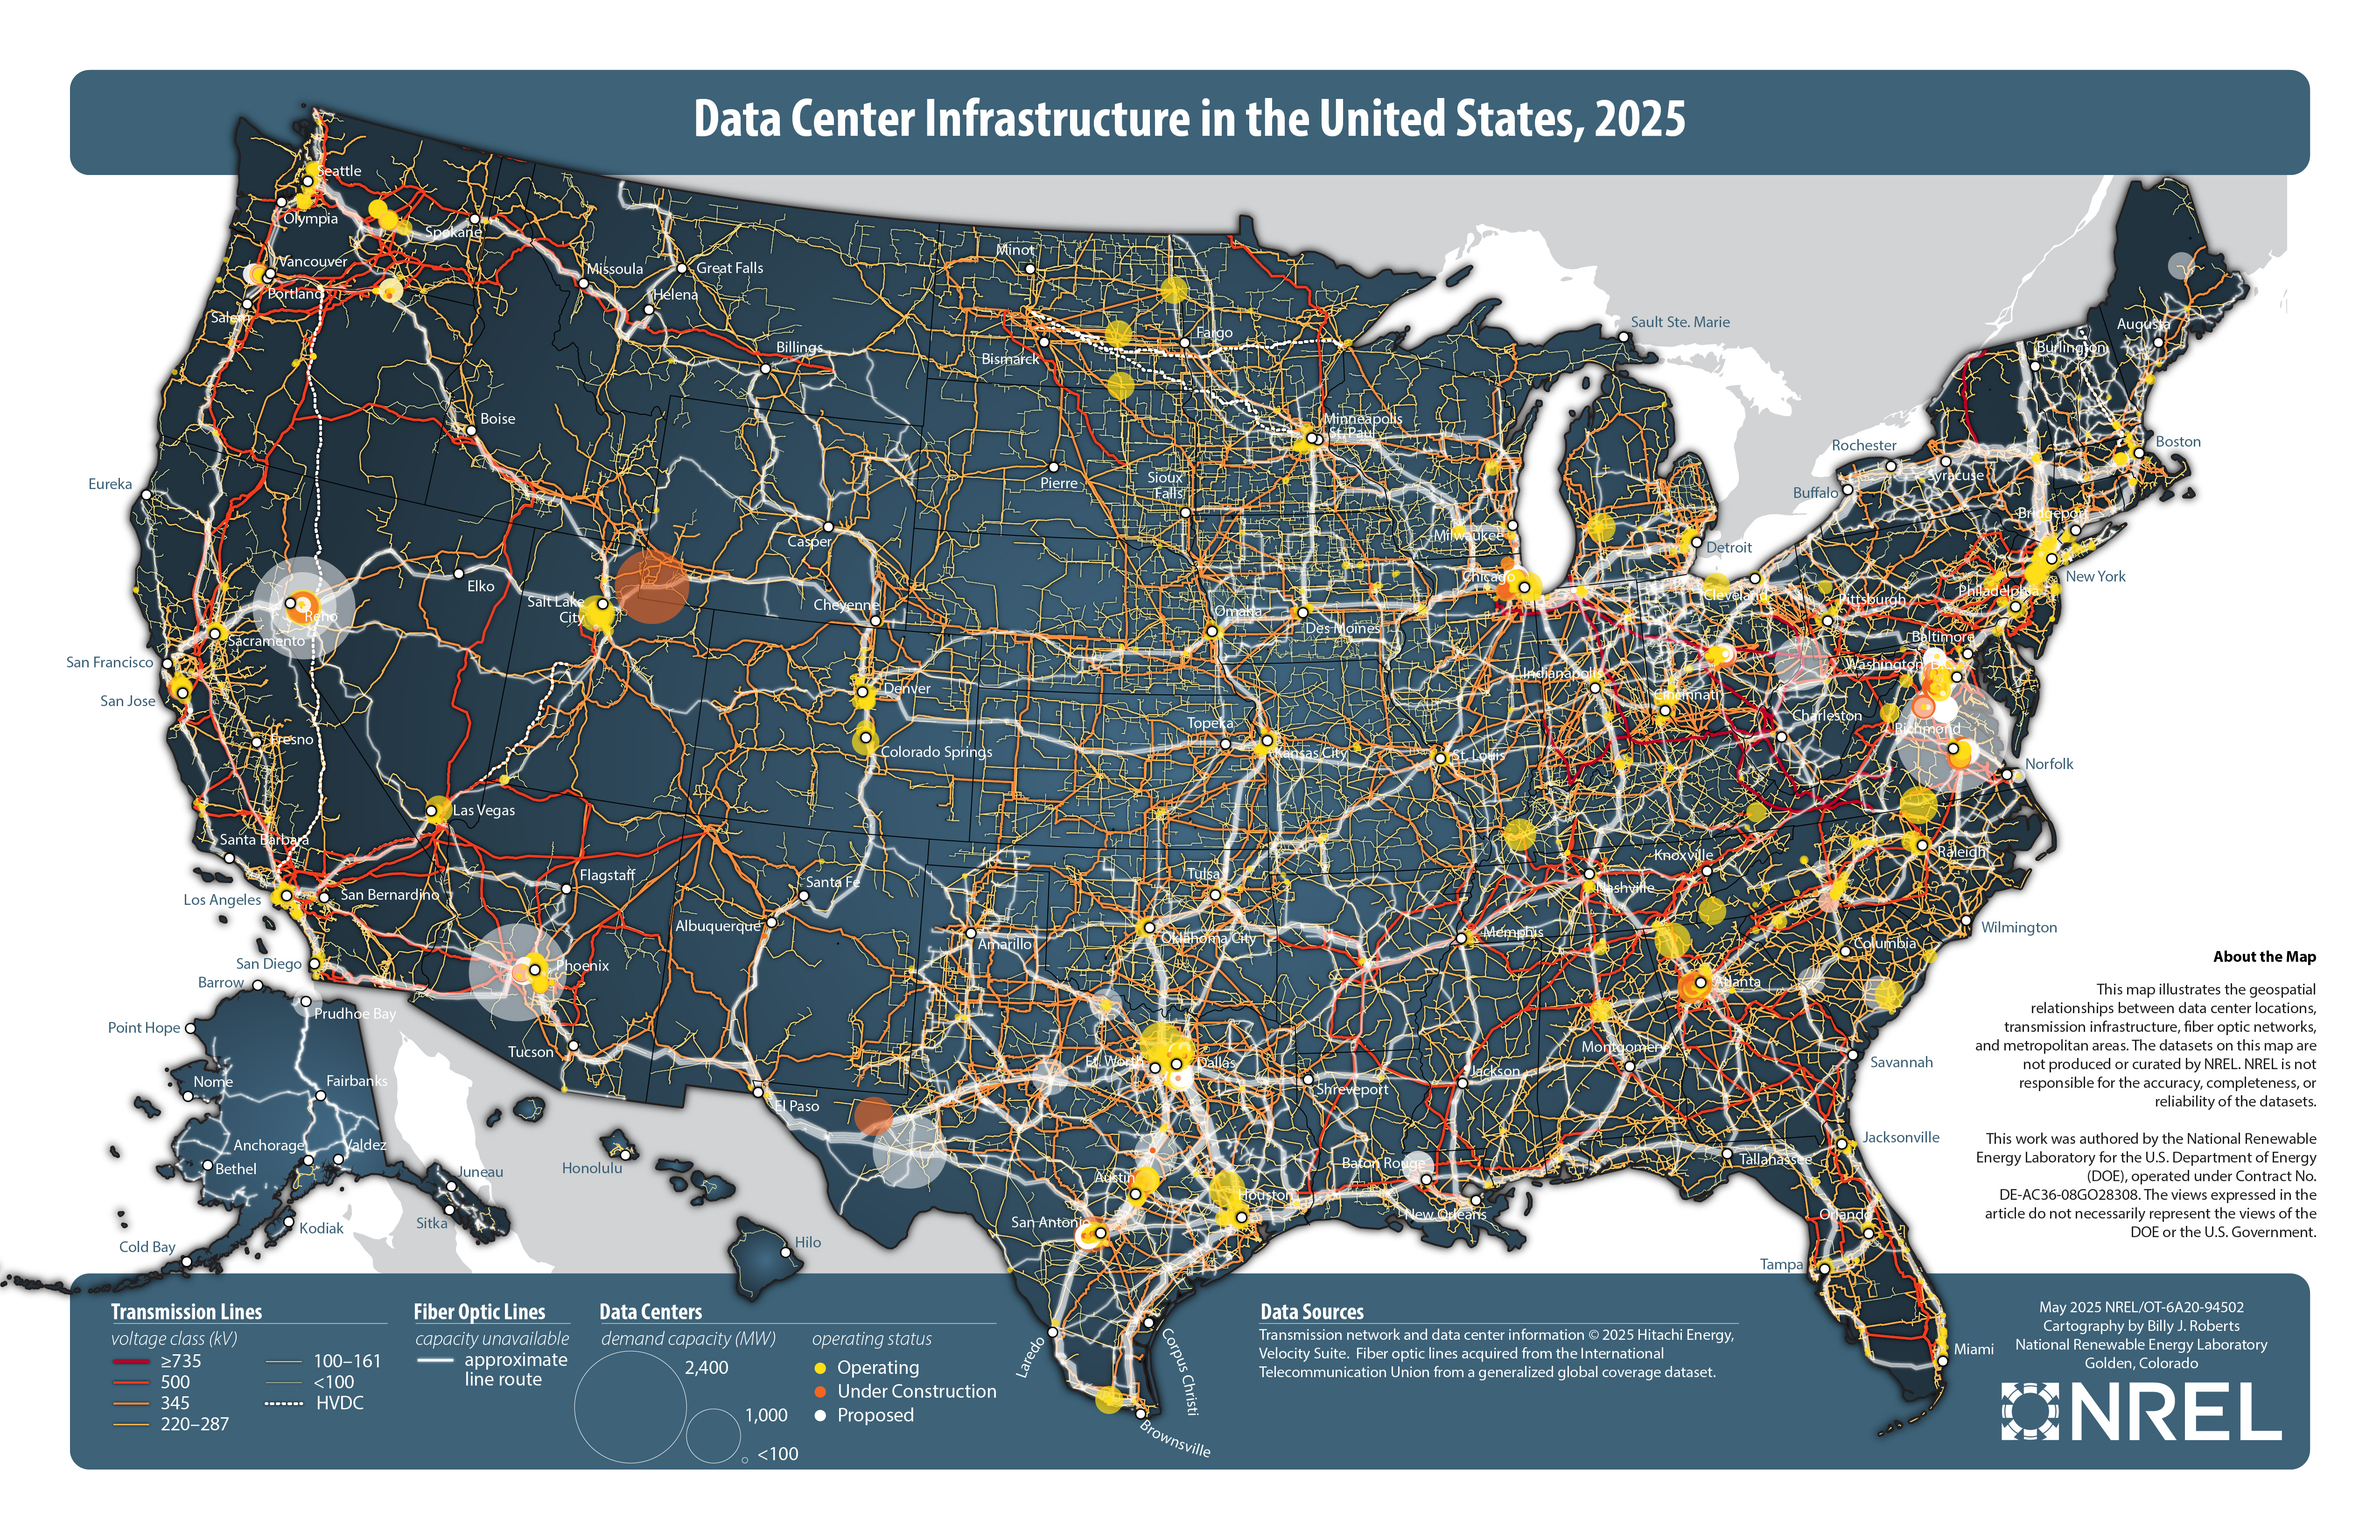
The NCSC's recommendation around passkeys is a useful example. Passkeys will not solve AI-enabled cyber conflict, but they remove one of the most common failure modes: reusable passwords that can be phished, sprayed, or leaked. The future-facing AI warning therefore loops back to boring security hygiene.
Infrastructure Is The AI Safety Test
Topics: NCSC, critical infrastructure, AI cybersecurity, GCHQ