Technology
ChatGPT adds Apple Messages plug-in for reading, drafting and sending texts on Apple Silicon Macs
ChatGPT can now interact with Apple Messages on Apple Silicon Macs through a plug-in that runs locally and requires Full Disk Access. Messages are read only after a specific request, stored locally by default and subject to a per-send confirmation unless the user deliberately disables it.
By Patrick T ·
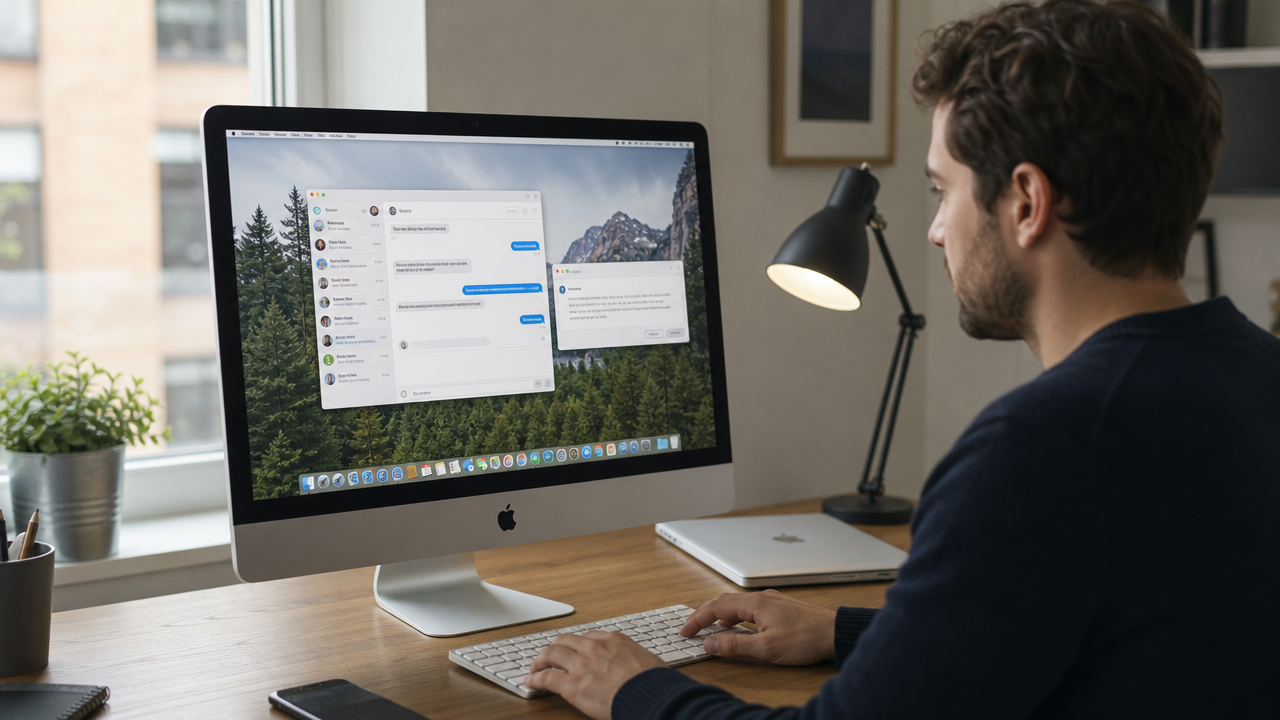
ChatGPT can now read, draft and send texts through Apple Messages on Apple Silicon Macs, extending the assistant into a system application that is usually treated as a private communications record. The plug-in runs locally, according to a TechCrunch report, and requires the user to grant Full Disk Access before it can interact with message data. It does not continuously ingest conversations. Messages are read only after a specific request, content is stored locally by default, and each send requires confirmation unless the user deliberately disables that safeguard.
The feature gives ChatGPT a way to move from composing text in a separate window to operating inside an existing messaging workflow. A user could ask it to find information in a requested conversation, prepare a reply or send a message through Apple Messages, subject to the plug-in's access and confirmation controls. The reporting brief does not establish whether the plug-in supports every Apple Messages feature, how it handles attachments or group conversations, or whether its behavior is consistent across all supported macOS versions. Those details matter because messaging is an operational system, not simply another document repository.
For OpenAI, the integration also places the product closer to the point where an assistant can take an external action. Generating a draft is reversible and easy to inspect. Sending a text changes a user's communication record and can reach another person immediately. The distinction explains why a per-send confirmation is significant even when the underlying model is not making a high stakes business decision. A mistaken recipient, an incomplete draft or a message sent at the wrong time can create consequences that are difficult to repair after delivery. TechCrunch report documents the reporting behind this account.
Local execution with broad macOS access
The plug-in's local operation changes the data path, but it does not remove the need for careful access management. Full Disk Access is a powerful macOS permission. Granting it allows an application to reach protected files and data that ordinary application permissions would not expose. The precise implementation boundary for this plug-in is not described in the available reporting, so it is not possible to conclude that the assistant can see every item covered by the permission. The operational point is narrower: users are being asked to authorize a broad system capability so that ChatGPT can perform a targeted messaging task.
That tradeoff will be familiar to Mac administrators. A local connector can reduce the need to upload message archives to a remote service and may make the integration work with existing desktop applications without a separate server deployment. It also moves responsibility toward the endpoint. The machine's user account, local permissions, application state and security controls become part of the system boundary. If a company permits the plug-in on managed Macs, its administrators may need to determine who can install it, how Full Disk Access is granted, whether the permission can be centrally audited and what happens when an employee leaves or a device is reassigned.
The default storage behavior is another important implementation choice. Message content remains local by default, according to the reporting brief. That reduces one category of exposure because the default workflow does not require creating a separate hosted message store. It does not answer every retention question. Local content can still be included in application logs, temporary files, caches or diagnostic reports unless the product explicitly excludes those locations. The available information does not specify the plug-in's retention schedule, encryption model, log contents or deletion controls, so organizations should treat those as open operational questions rather than assume that local means permanently isolated. OpenAI offers useful technical background for evaluating the claim.
The request based reading model is designed to limit background access. ChatGPT reads messages only after a specific request, rather than continuously scanning the inbox. That constraint can narrow unnecessary exposure and make the feature easier to explain to users. It also puts more weight on request interpretation. A vague instruction such as asking for the latest update from a contact may require the system to identify a conversation, determine which messages are relevant and decide what information to present. The brief does not provide the plug-in's exact confirmation or disambiguation behavior for those read operations.
Sending is more clearly bounded. The system keeps a confirmation for each send unless a user deliberately disables it. That default creates a final human checkpoint between an assistant's proposed action and delivery. It adds friction, particularly for repeated or routine messages, but it also makes the cost of a model error visible before the message leaves the device. If a user turns the control off, the workflow becomes faster while the remaining safeguards become less clear from the available information. The choice is therefore a policy decision as much as a convenience setting.
A desktop connector with enterprise consequences
The integration also works with Codex and ChatGPT Work, which broadens the audience beyond people using a consumer assistant for occasional personal texts. In a work setting, the same capability could help prepare customer updates, coordinate appointments or draft internal communications. It could also create problems if an employee allows a personal conversation, confidential thread or regulated information to become part of an automated workflow. The reporting does not establish which workplace controls apply to the plug-in, whether administrators can disable sending, or how usage is recorded in ChatGPT Work.
The distinction between a product feature and a supported enterprise control will matter. An organization can tolerate a user confirming an occasional message on a personal Mac. It may require different controls when the device contains customer records, executive communications or information subject to contractual restrictions. A local plug-in may be easier to deploy than a custom integration, but ease of deployment is not the same as governance. The business case depends on access policy, audit requirements, support ownership and the cost of investigating an incorrect or unauthorized message.
The feature is also separate from a conventional server side messaging integration. A developer using the OpenAI API would normally design the credentials, data flow, application permissions and action controls for a service of its own. This plug-in instead connects an assistant to a user's local Mac session and existing Messages account. That can lower integration work for an individual, but it leaves less room for a company to define its own interface, approval flow and retention model unless the product supplies those controls.
Reliability will be judged at several layers. The plug-in must identify the right conversation, interpret the request, generate an acceptable draft and hand the action to Apple Messages without losing context. A failure in any one layer can produce a poor result even if the model's prose is accurate. Local execution may reduce dependence on a separate connector service, but it does not eliminate failures caused by permissions, application updates, account state or a Mac that is offline. The available reporting does not provide performance measurements, supported version details or recovery behavior, so organizations should avoid treating the feature as a dependable unattended communications system.
That limitation is especially relevant when users disable the send confirmation. A deliberate opt out may suit a tightly defined personal workflow, but it changes the system from assisted composition to a more autonomous action path. The risk is not limited to malicious behavior. Misread instructions, stale conversation context, a contact with a similar name or a generated sentence that changes the intended tone can all produce an unwanted result. A practical deployment would need clear rules about which tasks can be automated and which must remain subject to review, even if the software allows a broader setting. For broader context, OpenAI API outlines the relevant standard or institution.
The privacy design can be evaluated in the same operational terms. The local default and request based reading reduce routine collection, while Full Disk Access expands the potential reach of the desktop client. Confirmation limits the final action, while the ability to disable it removes that barrier by choice. None of those controls, viewed alone, answers how a workplace should classify the tool. Administrators still need evidence about logs, retention, permission management, update behavior and the treatment of data passed between ChatGPT, the plug-in and Apple Messages.
Those questions align with the control categories in the NIST AI Risk Management Framework, including governance, measurement and management of risks across the system lifecycle. The framework does not determine whether this plug-in is safe for a particular organization, but it provides a useful way to examine the complete workflow rather than focusing only on the model. A review should include the endpoint permission, the source conversation, the generated draft, the human approval step and the delivered message. It should also define how incidents are detected and who can revoke access.
For individual Mac users, the immediate decision is whether the convenience of asking ChatGPT to work with Apple Messages justifies granting Full Disk Access. Users should understand that the feature is local by default, that a specific request is required before messages are read and that sending normally remains subject to confirmation. They should also know that disabling confirmation changes the risk profile. The reporting brief does not indicate that the plug-in reads messages without a request or stores their content remotely by default, and those limits should be preserved in any explanation of the product.
For ChatGPT customers, the release signals a broader direction for desktop assistants: access to existing applications can be more valuable than another isolated chat window, but it also makes permissions and action boundaries part of the product experience. The plug-in's local design and confirmation default address some of that problem. They do not remove the need for users and administrators to understand what has been authorized, what remains on the Mac and what happens when a request moves from drafting to sending. NIST AI Risk Management Framework helps place the issue within its wider policy and engineering context.
The practical test will be whether those controls remain understandable under routine use. If users can identify the requested conversation, inspect the proposed text and see exactly when a message is about to be sent, the integration has a clear operating model. If permissions, storage or confirmation settings become invisible after setup, the same capability will be harder to govern. On Apple Silicon Macs, ChatGPT is now positioned to act on messages as well as discuss them. The value of that change will depend less on the novelty of sending a text than on how reliably the surrounding system keeps the user in control.
Topics: ChatGPT, Apple Messages, OpenAI, Mac, AI tools