Analysis
Snowflake Backs Dust and Gray Swan as Enterprise AI Spending Moves Beyond Models
Snowflake Ventures is highlighting investments in Dust and Gray Swan as companies demand governed data, reusable agents and runtime security before moving AI from pilots into production.
By Elvin C ·
Snowflake Ventures is putting a sharper definition around its enterprise AI investment thesis, arguing that the next valuable layer will sit between foundation models and business applications. The company highlighted portfolio firms Dust and Gray Swan as examples of the infrastructure required to make agents useful at work: governed access to company knowledge, reusable workflows, identity-aware controls and security that remains active while a model is taking action.
The argument reflects a change in buying behavior. Companies spent the first phase of generative AI comparing models and running isolated pilots. Production exposes less glamorous questions. Which records can an agent retrieve? Can it distinguish a draft from an approved policy? Who can authorize a tool call? What happens when the model changes? These controls rarely appear in a benchmark, but they determine whether legal, security and operations teams allow a deployment to expand.
The Missing Middle of the AI Stack
Snowflake describes a layer built around flexible model access, security and AI-native workflows. It has an obvious commercial interest in that architecture. If enterprise agents need one governed source of truth, Snowflake wants its data platform to occupy that position. The venture portfolio can extend the company’s reach into the interfaces and control systems customers use above the database.
Dust builds organizational agents that search company knowledge, connect through Model Context Protocol servers and coordinate reusable skills across teams. Its value proposition is not a proprietary frontier model. It is the ability to use different models without rebuilding the knowledge and permission layer around every one of them. That portability becomes more valuable as model prices and capabilities change quickly.
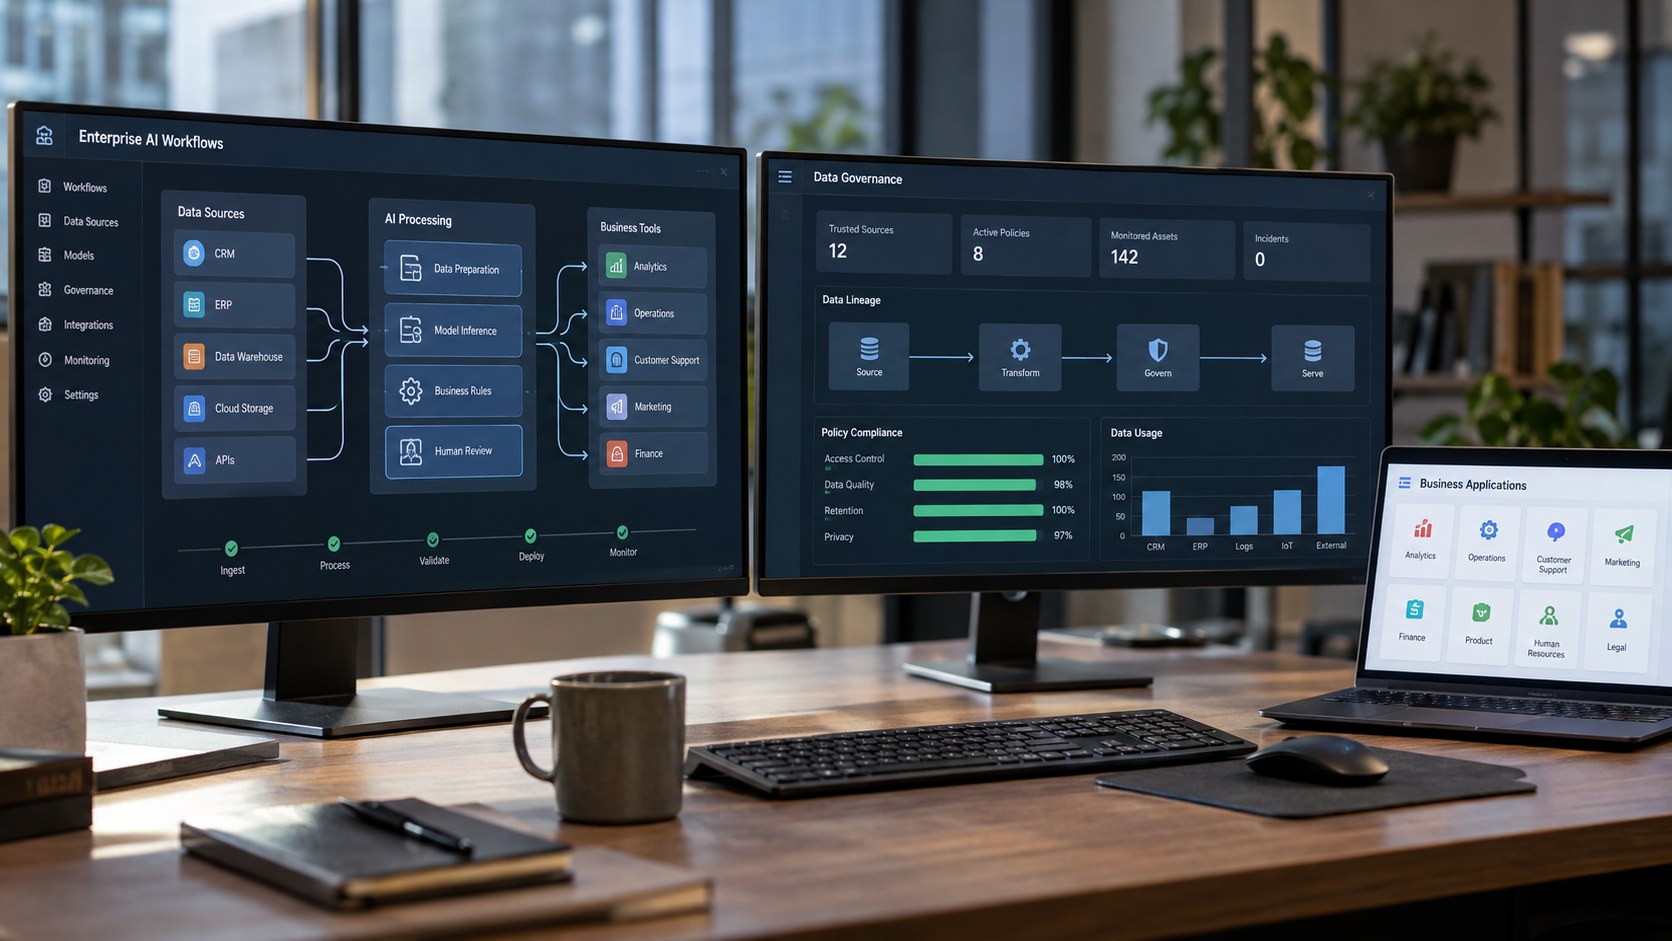
Gray Swan works on runtime protection, testing systems for vulnerabilities and monitoring how models behave after deployment. Static evaluation is not enough for an agent that encounters new documents, tools and adversarial instructions every day. Runtime defenses can identify prompt injection, policy violations and suspicious action sequences, although they must avoid blocking so much legitimate work that users route around them.
Together, the investments reveal where enterprise value may accrue if foundation models become more interchangeable. Companies will still pay for intelligence, but the durable system of record may live in the data, identity and workflow layer. A vendor that owns that layer can swap underlying models while retaining the customer relationship and the operational context that makes each deployment useful.
Governance Must Be Enforced, Not Described
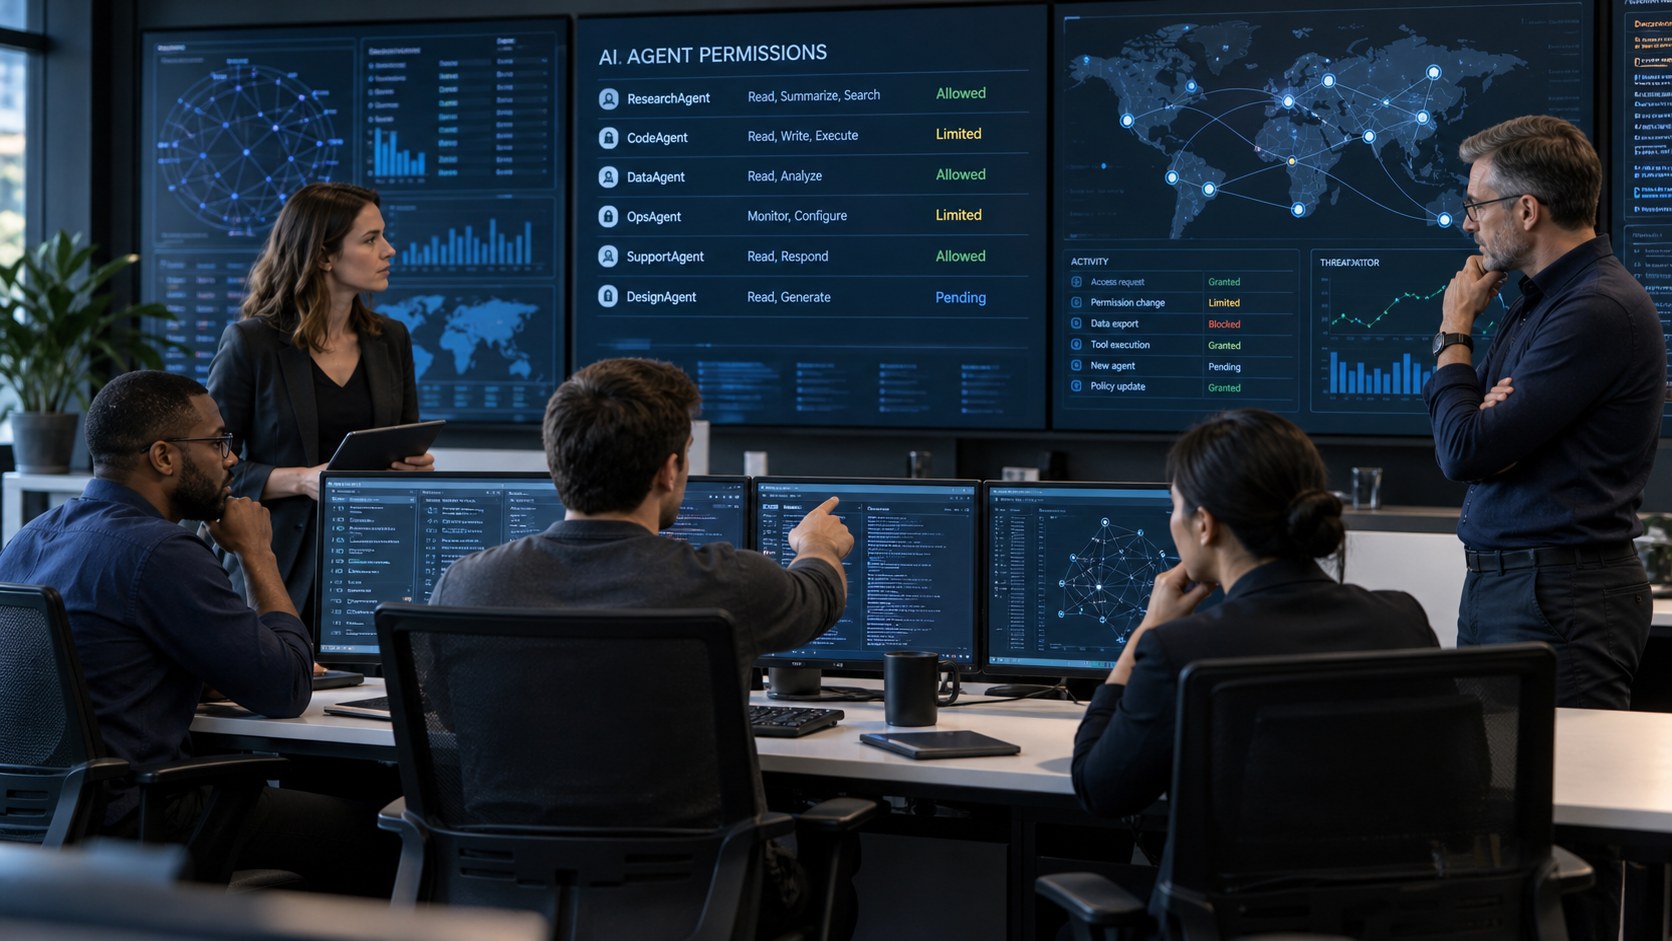
Many AI products advertise governance as a dashboard. Real governance changes what the system can do. A sales agent should not retrieve payroll records because a prompt asks creatively. A coding agent should not deploy to production without the required approval. Policy needs to be enforced by identity and tool boundaries outside the language model, with logs that let an investigator reconstruct each action.
MCP has accelerated integration by giving models a common way to discover and call tools. It also expands the attack surface. Every server can become a path to sensitive data or side effects, and descriptions supplied by tools can influence model behavior. The protocol’s security guidance emphasizes consent, authorization and careful handling of tool metadata, but enterprises still need implementation-specific controls.
The data layer creates its own complexity. Enterprise information is duplicated across warehouses, document stores, messaging systems and SaaS applications. Permissions that work for a human interface may not translate cleanly to an agent making hundreds of retrievals. Companies need to preserve source-level access rules and provenance rather than copying everything into a new index with broader permissions.
Evaluation must move from response quality to completed work. Useful measures include accepted tasks per hour, correction time, unauthorized-access attempts, tool failures and the cost of recovery. An agent that drafts faster but creates more review work may be less productive. A security layer that catches every attack but blocks common workflows may be safe only because nobody uses it.
An Investment Thesis Becomes a Platform Strategy
Buyers should avoid solving governance by purchasing a product before they have defined the policy. Software can enforce who may call a tool or retrieve a record, but leadership must decide which decisions remain human, what evidence justifies automation and who owns a failure. A platform installed over unresolved accountability will make the ambiguity faster, not remove it.
The emerging category will be tested during incidents. When an agent sends the wrong message, changes a customer record or exposes restricted data, operators need one timeline across the model, retrieval layer and business application. Vendors that export complete, interoperable audit records will be more valuable than those that keep every event inside a proprietary dashboard.
Snowflake can benefit even if Dust and Gray Swan remain independent. Integrations make its platform more attractive as the governed center of an agent architecture. Portfolio relationships can also show Snowflake where customers are struggling before those needs become core product features. The risk is that buyers resist assembling another crowded stack of overlapping AI tools.
Consolidation is likely. Cloud providers, data platforms, security companies and application vendors all want to own agent governance. Customers will prefer fewer control planes, but no single vendor can cover every model and business system equally well. Open interfaces and portable audit data will matter because today’s convenient bundle can become tomorrow’s lock-in.
Regulation will strengthen demand for evidence. The NIST AI Risk Management Framework encourages organizations to map, measure and manage AI risks across a system’s lifecycle. Products that can show lineage, permissions, evaluation and incident history will have an advantage over systems that offer only broad assurances.
Snowflake’s thesis is persuasive because it focuses on the part of enterprise AI that models cannot solve by becoming smarter. Organizations still need to decide who owns a workflow, which data is authoritative and what happens when automation is wrong. Dust and Gray Swan are bets that those decisions can become software. The winners will be the companies that make control visible without turning every useful action into a bureaucratic queue.
Topics: Snowflake, Dust, Gray Swan, enterprise AI, AI agents